Built for teams that answer to someone.
The controls a security review asks for, in plain terms. Roles and teams, a policy document you can read, approval levels, break-glass for emergencies, and an audit log of everything.
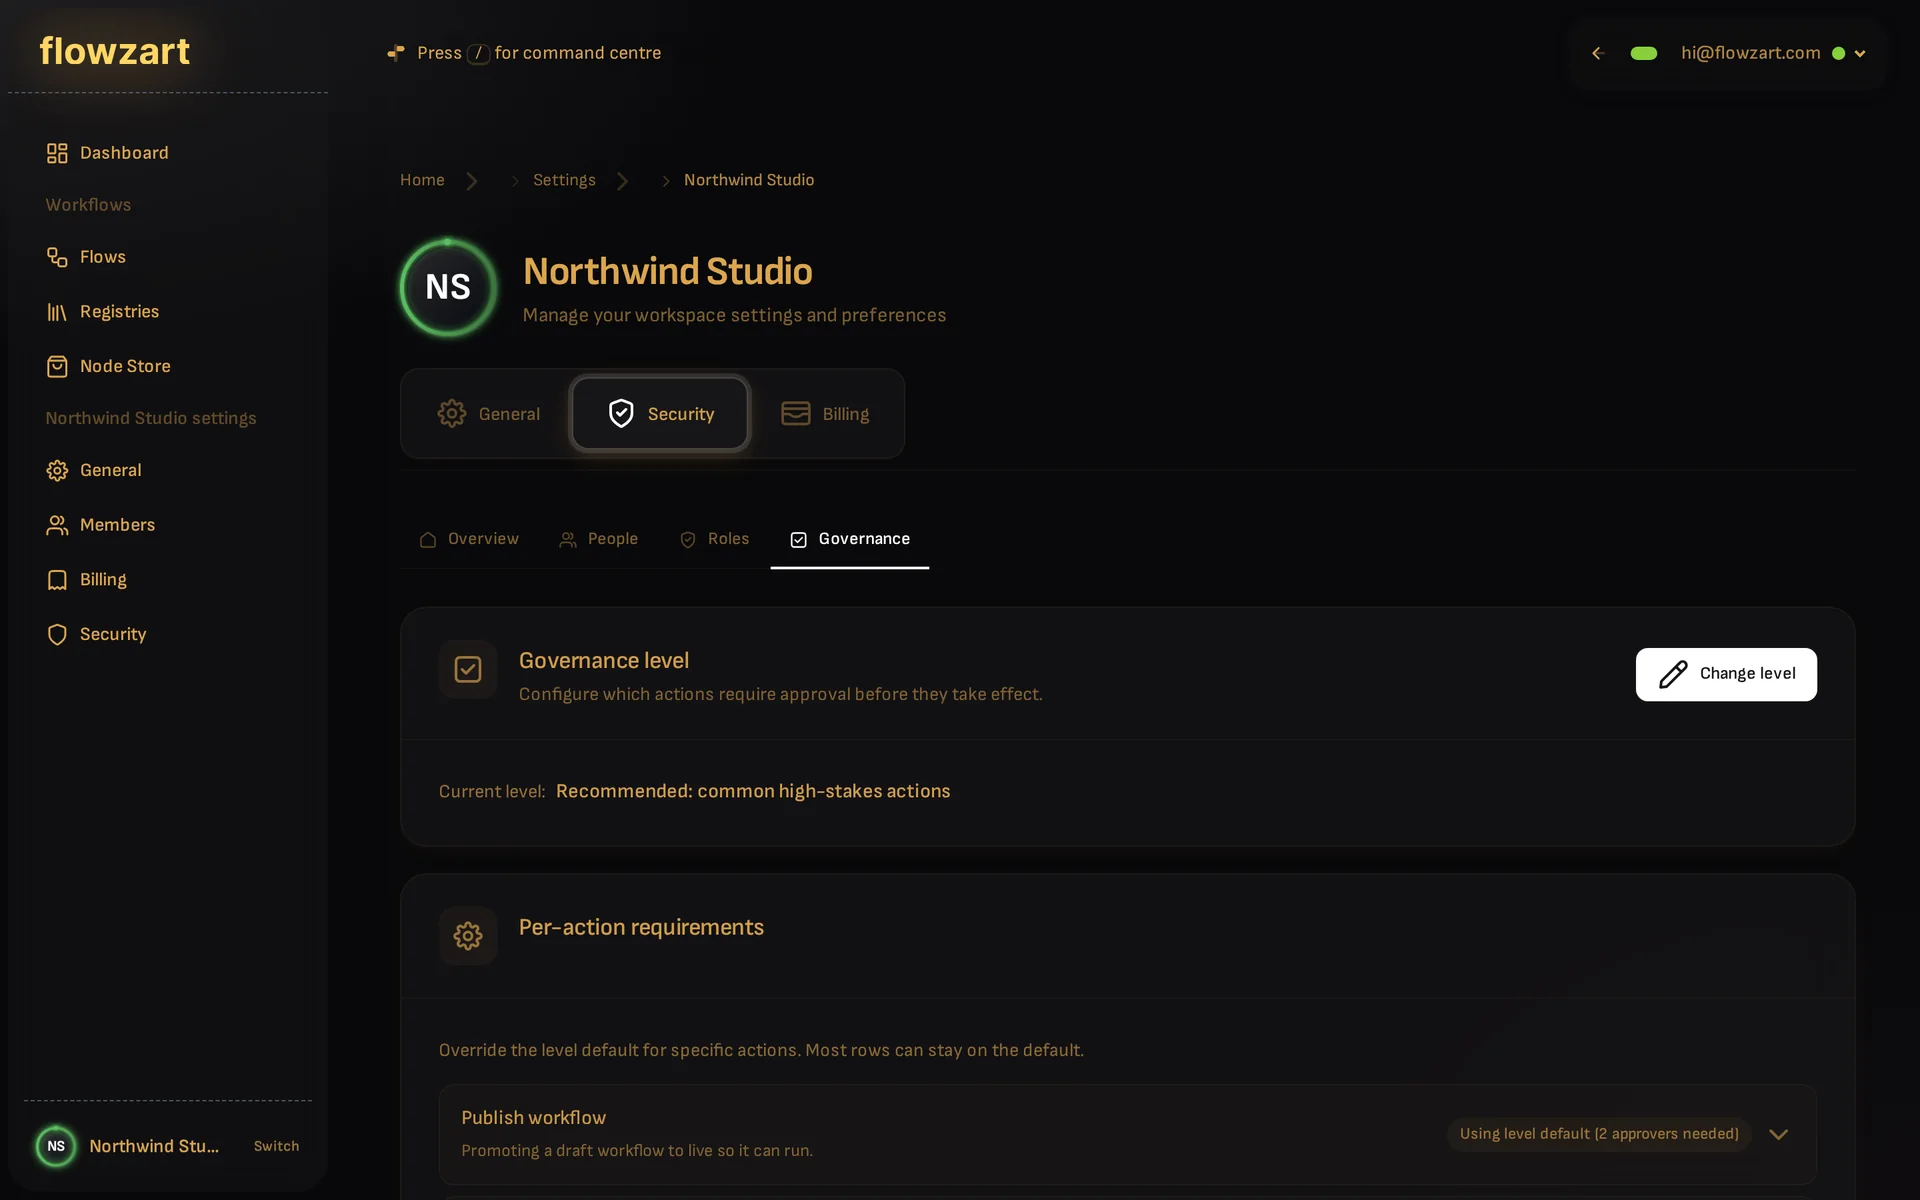
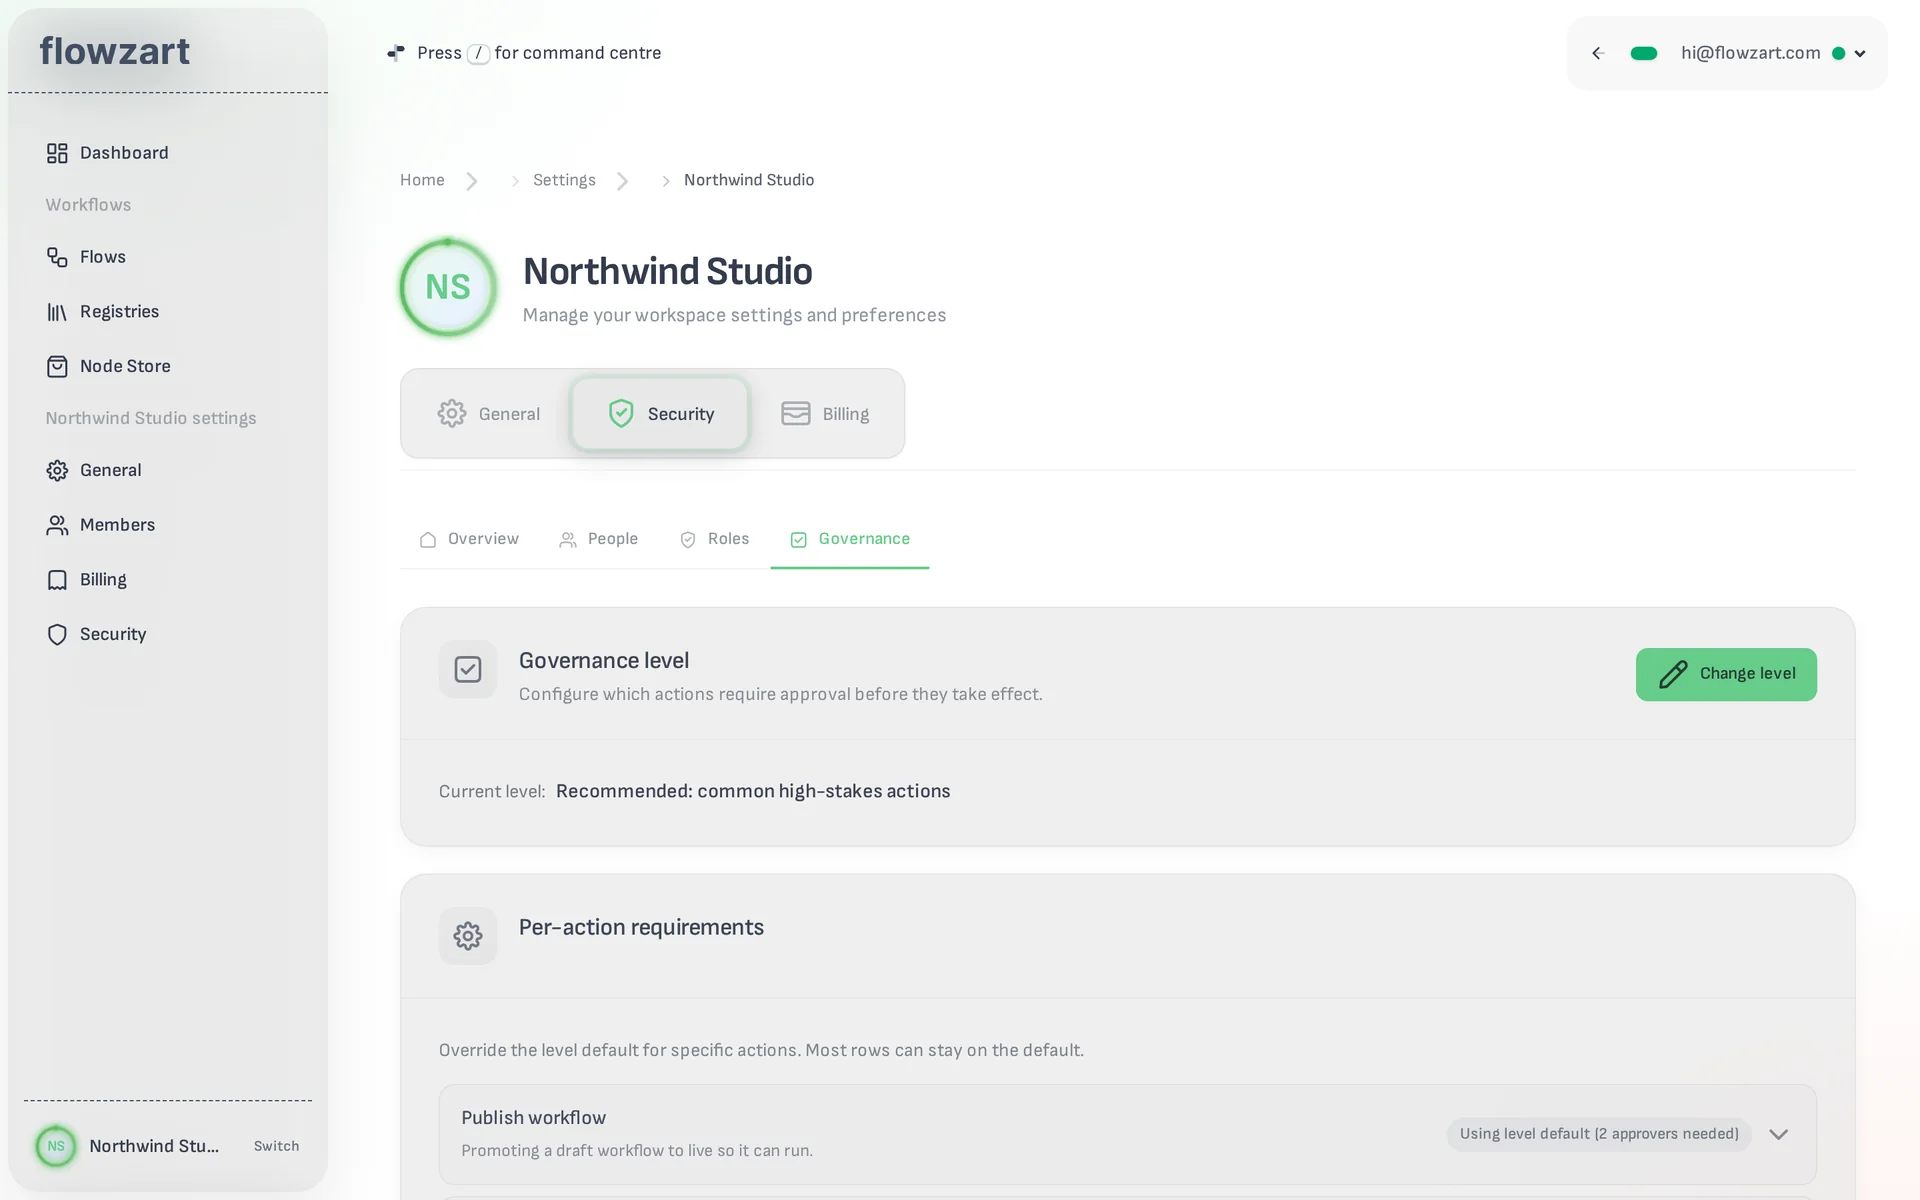
Recommended: common high-stakes actions
- 01
A policy you can read
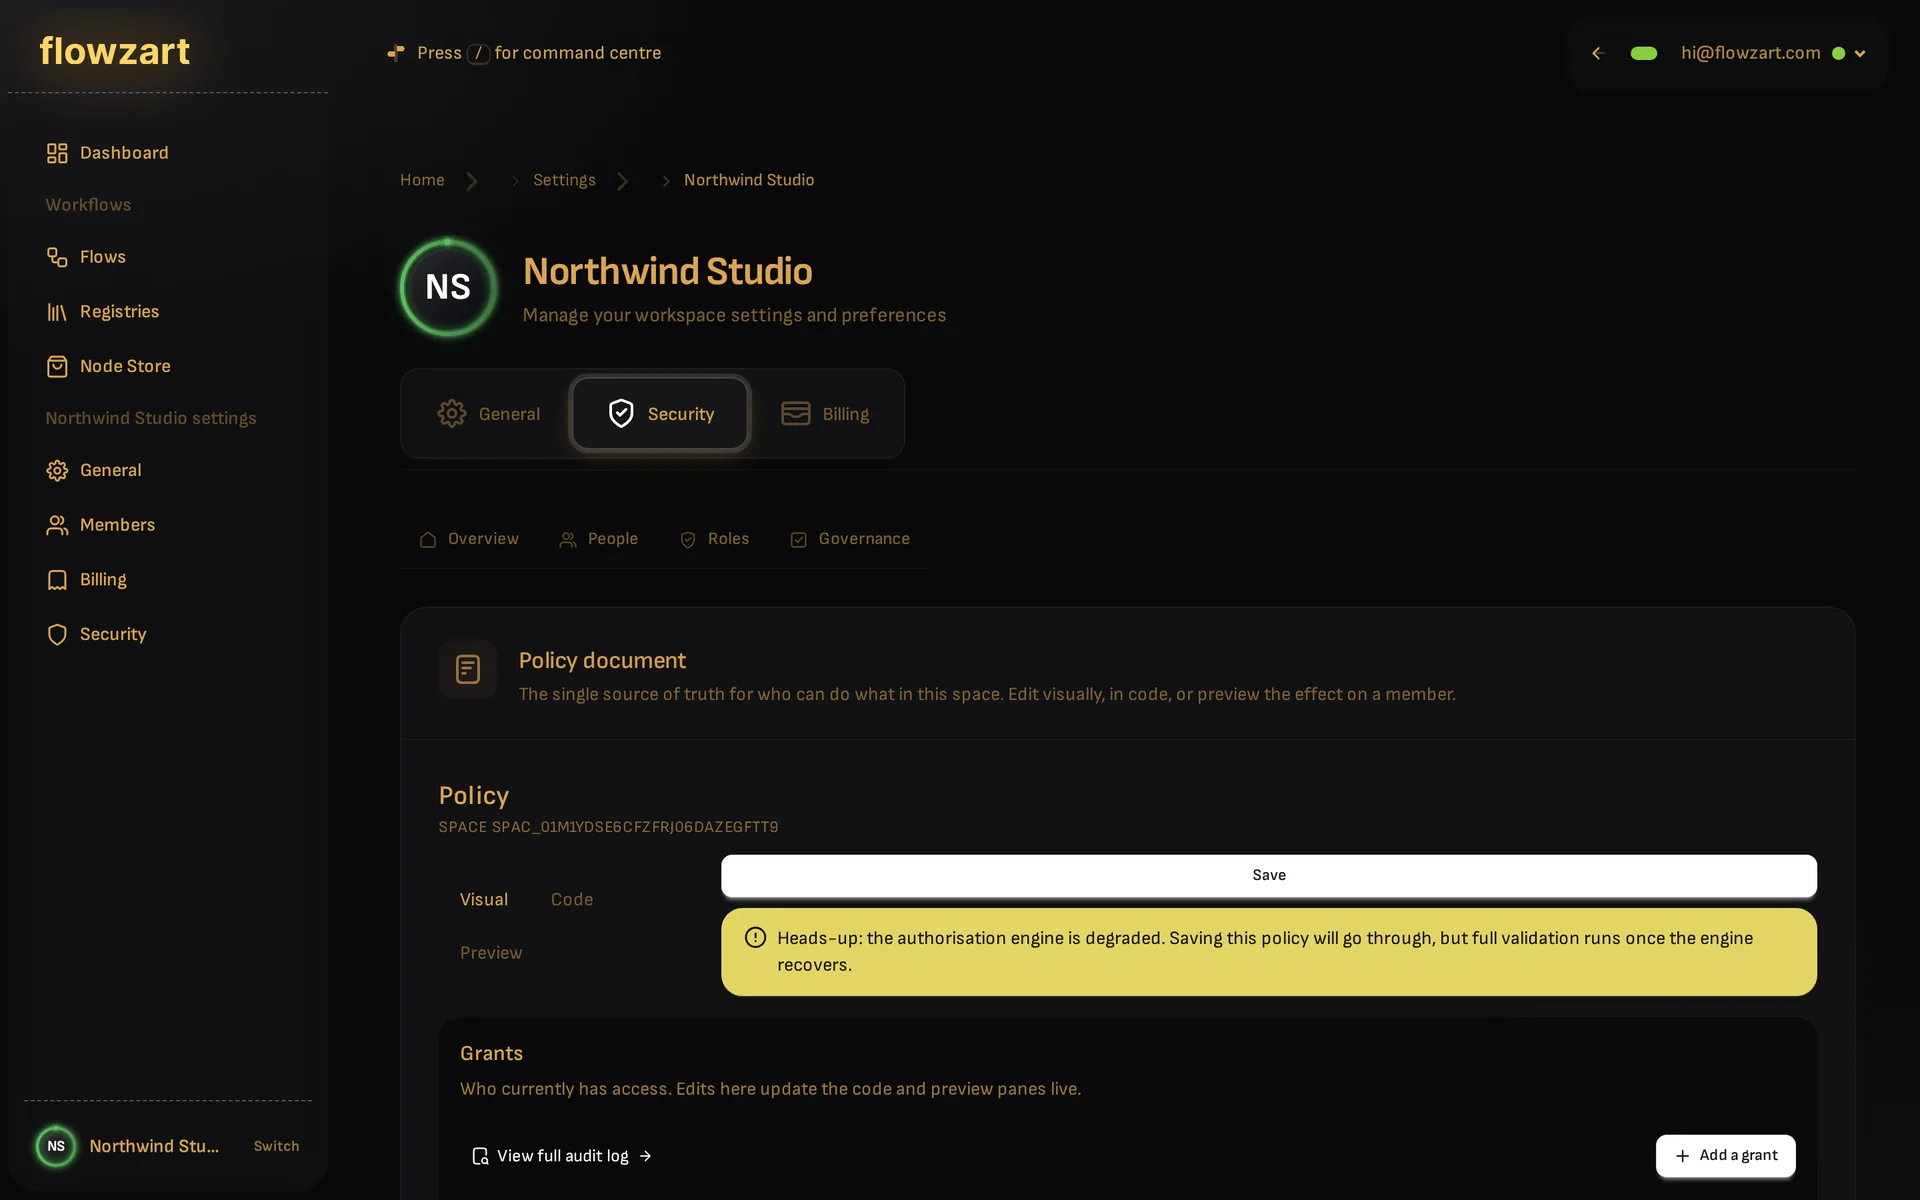
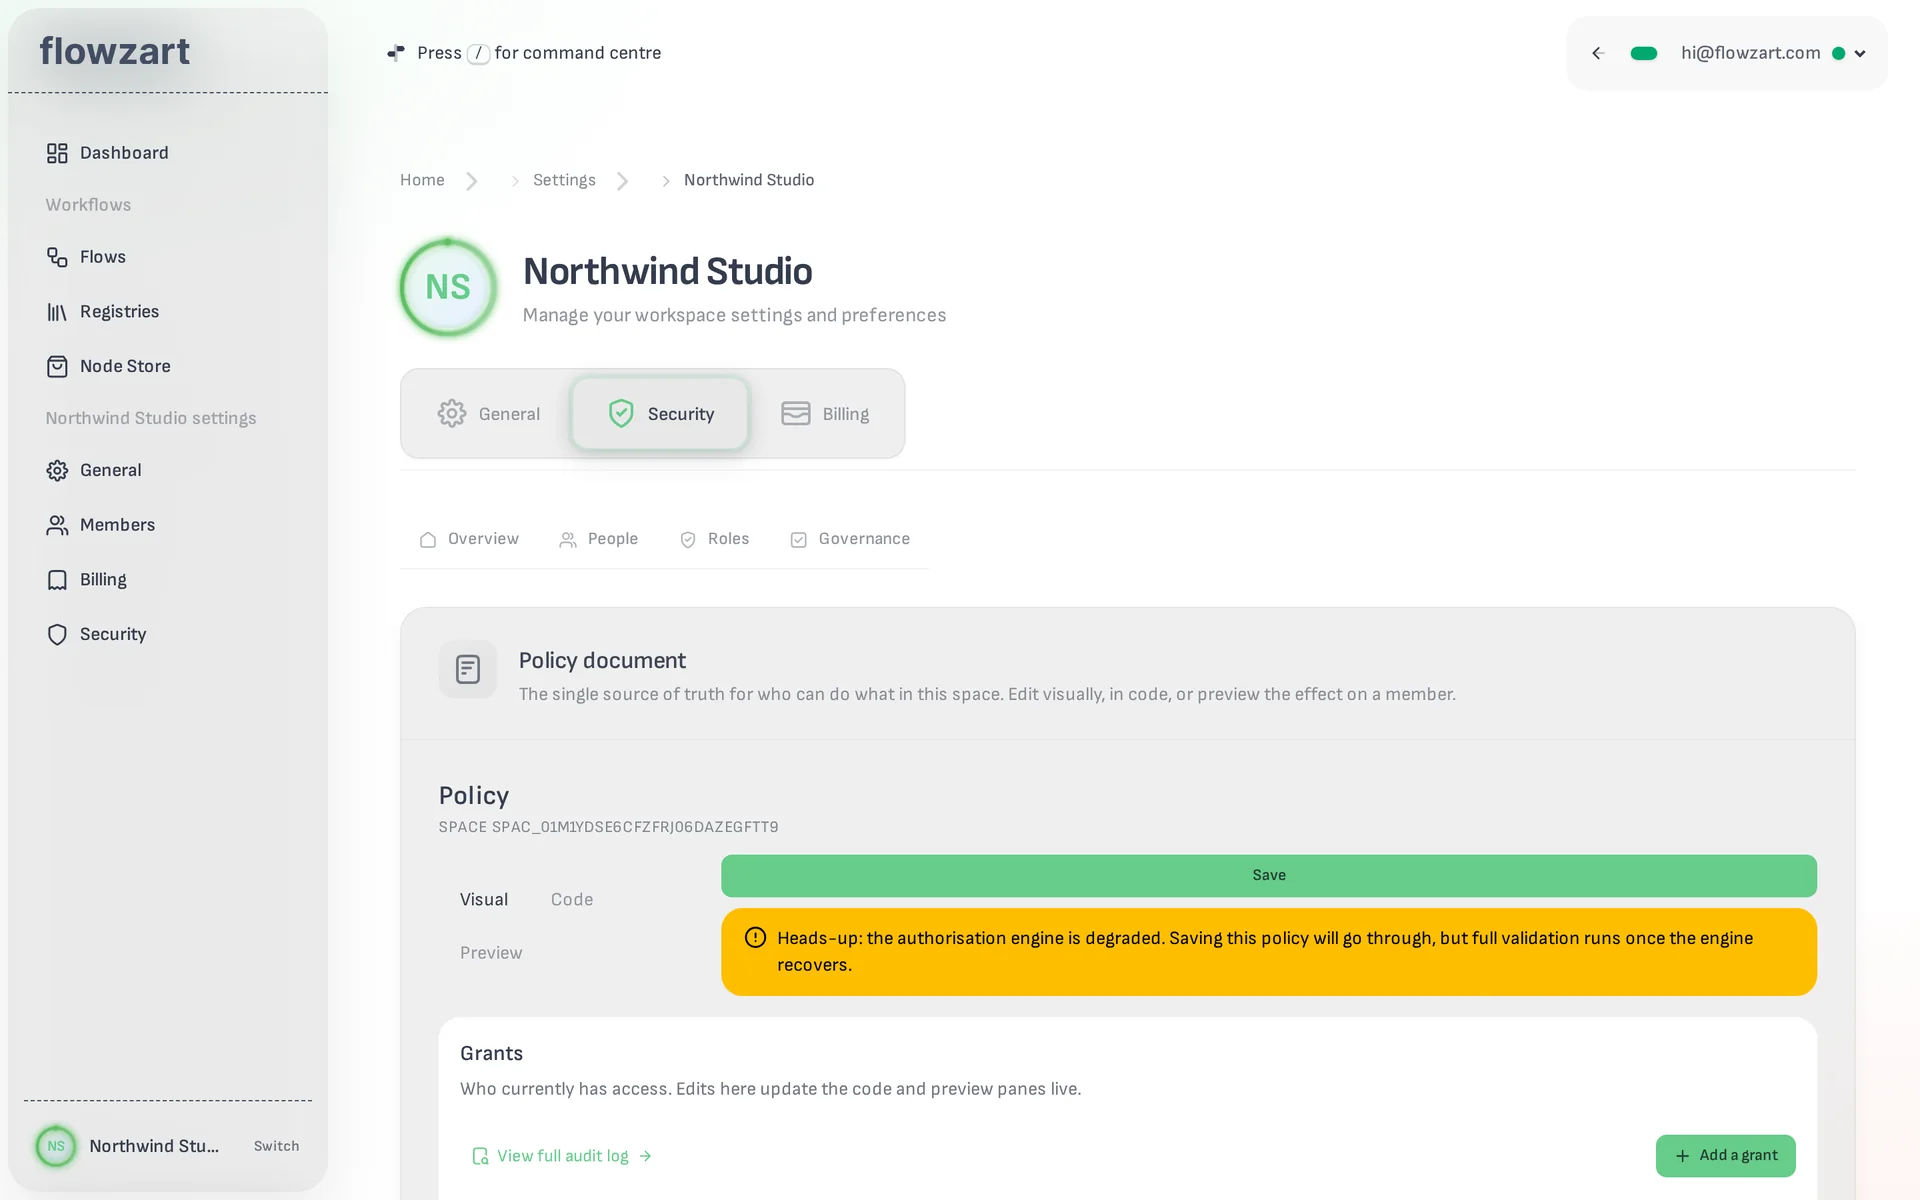
The single source of truth for who can do what, in one place. The visual editor and the code view edit the same document; the preview shows what a given member can do before you save.
- 02
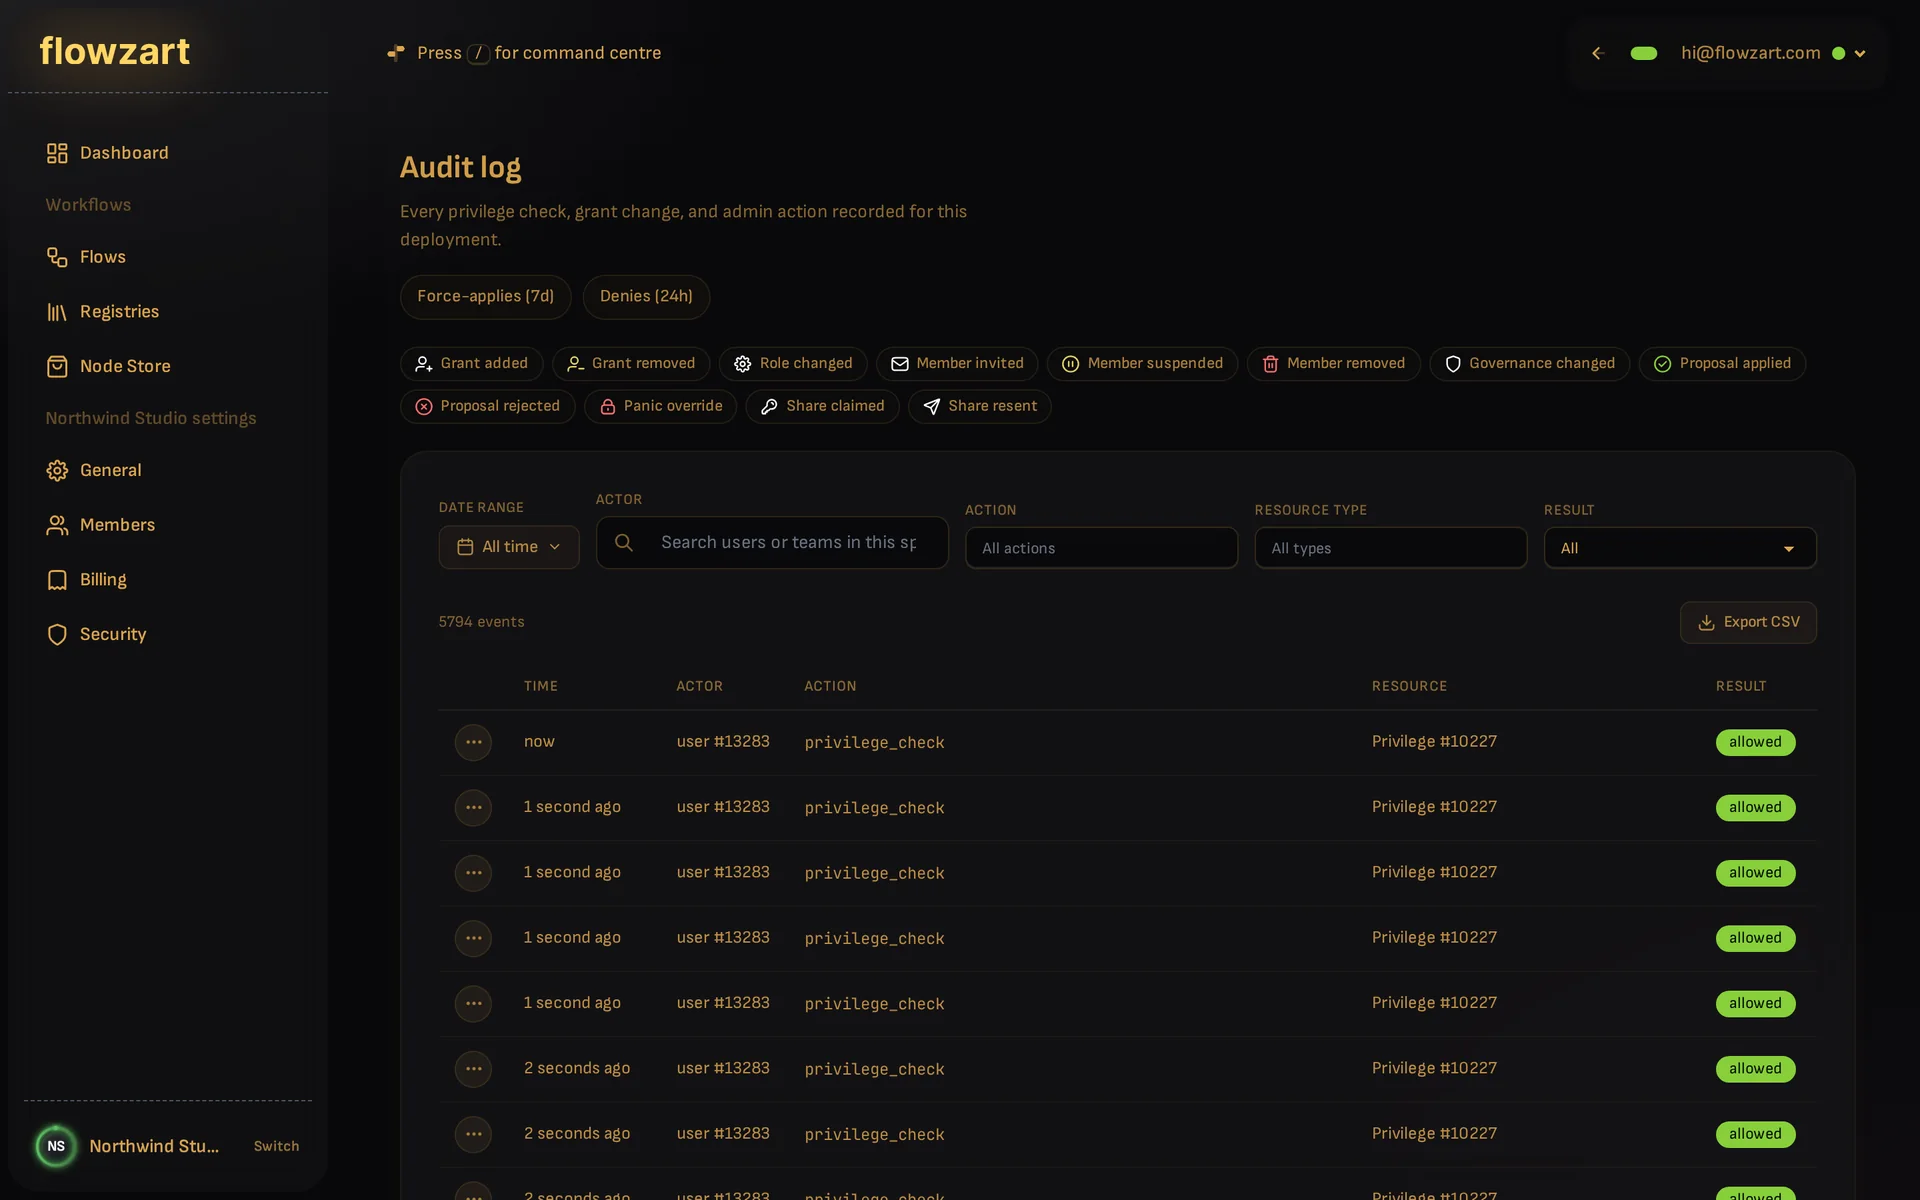
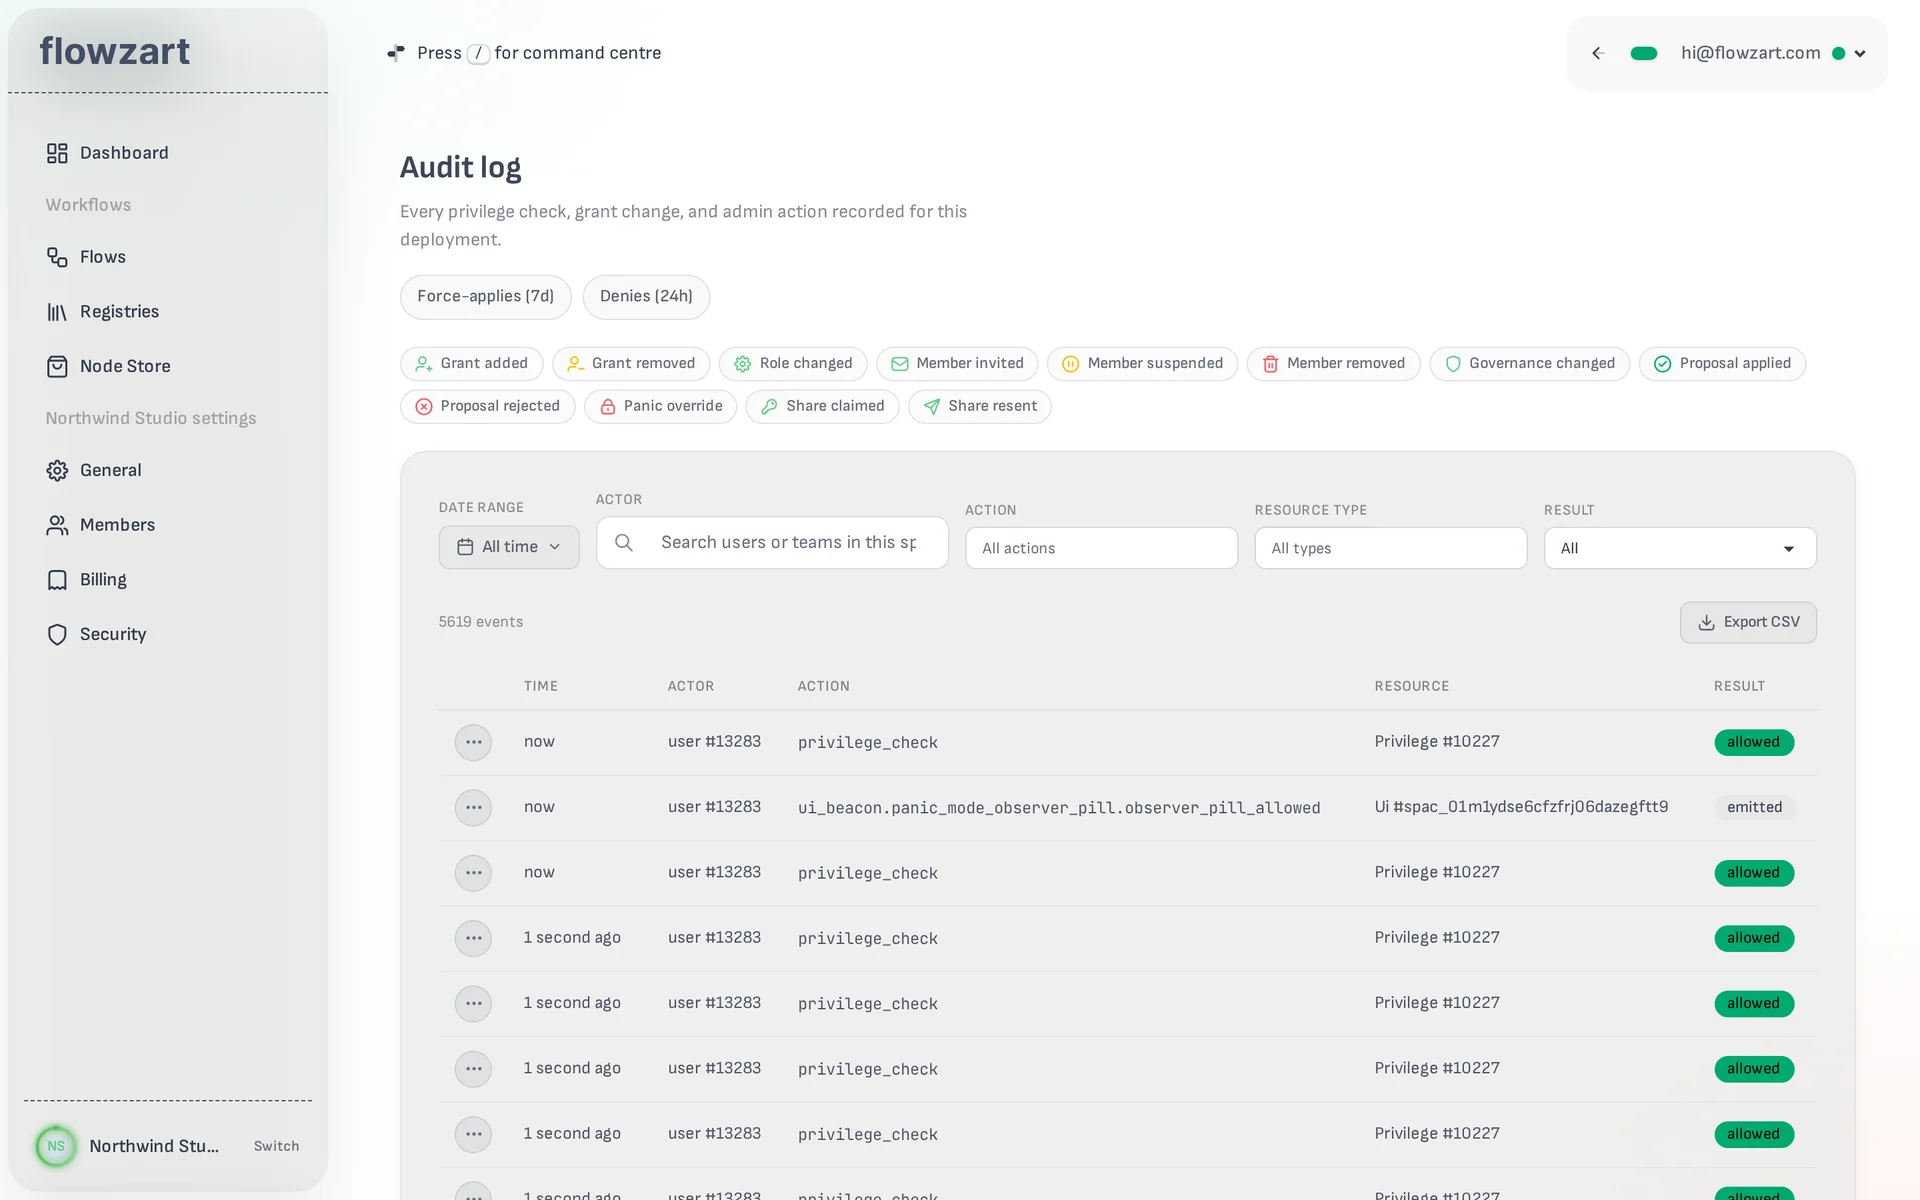
Everything, on the record
Grants, role changes, invitations, proposals, overrides. Filter it, or export the lot.
Roles, teams, service accounts
Owner, admin, editor and viewer cover most teams; custom roles bundle permissions when they do not. Teams group people; service accounts give automations an identity of their own.
One policy document
Who can do what in a space lives in one document. Edit it visually or in code, and preview the effect on any member before you save.
Approval levels
Off, light, strict, or custom per action. Raise the level and the actions you choose need approval before they take effect.
Break-glass
For the day something must be overridden, a ceremony brings the key's share holders together to mint a scoped, time-bound override. Every use is on the record.
Panic mode
In an emergency, a holder of an override can switch it on and every action they take applies the override until they exit. Everyone in the space can see it is on.
The audit log
Every privilege check, grant change and admin action, filterable by actor, action and result, exportable as CSV.
Ready when you are.
Join the waitlist for a Concert Ticket, or see how it works right now.